Here is the rule that should be compulsory: no bank may let a texted code be the only second check on a login or payment. That is an SMS OTP ban, and four markets already enforce one. Britain and the US only advise it. The objection, that a ban shuts out people without smartphones, is answered in the US government's own identity rulebook.
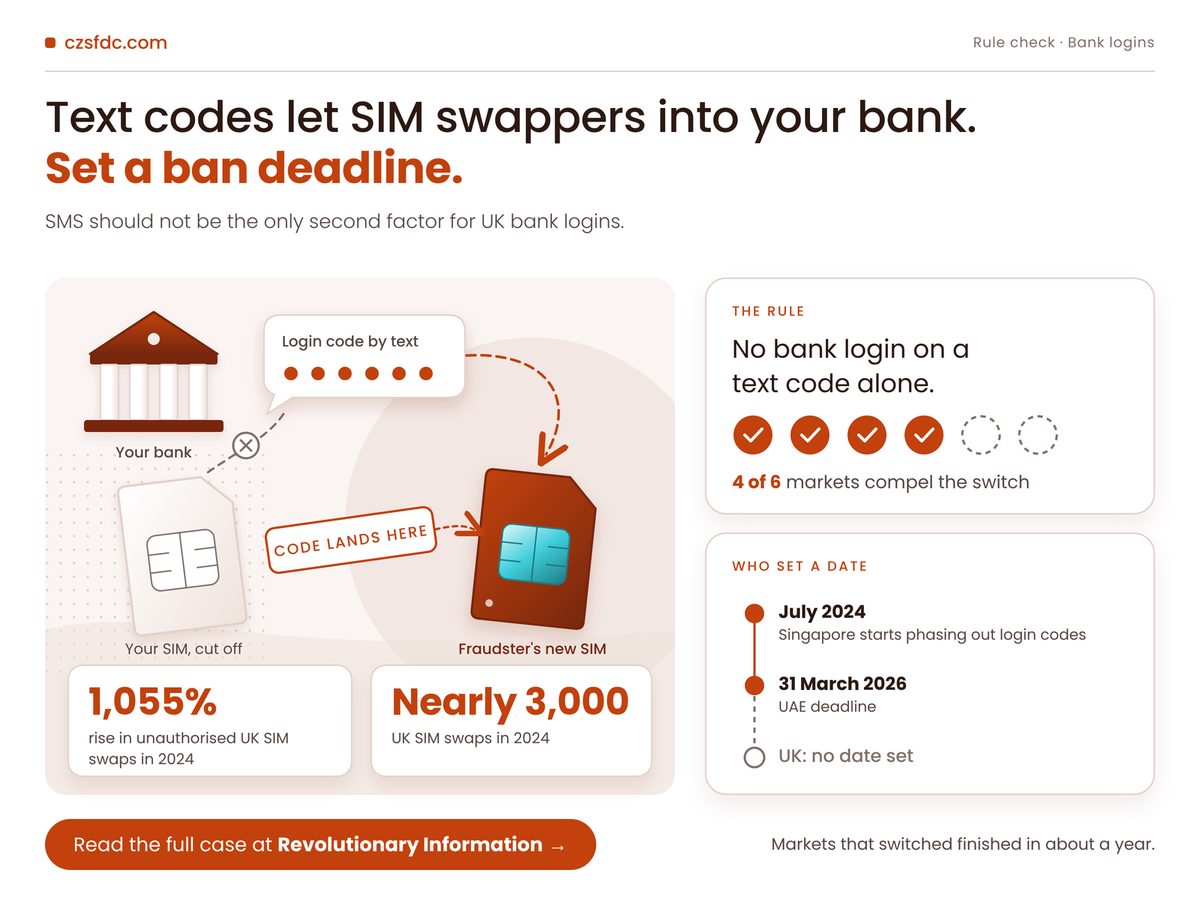
Picture what it prevents. A fraudster talks a mobile shop into moving your number to a new SIM, your phone loses signal, and your bank's next code lands in their hand.
TL;DR: Four markets force banks off text codes; UK and US customers must make the switch themselves.
- The UAE set 31 March 2026 for banks to drop SMS and email codes.
- NIST says texted codes are not phishing-resistant but keeps alternatives open to everyone.
- A synced passkey on your current phone meets NIST's middle bar at no extra cost.
- Count logins that accept a text code alone: one SIM swap opens all of them.
Why is SMS OTP not secure enough for bank logins?
A texted code proves only that someone controls your phone number, and both the number and the code can be taken from you without touching your handset, through a SIM swap or a fake login page.
NIST SP 800-63B-4, the US federal identity guideline dated August 2025, says out-of-band authentication "is not phishing-resistant": type a texted code into a fake bank page and the attacker relays it, however fast you act. Telling people to be careful with codes is outdated advice.
It also classes SMS codes as "restricted" and tells services to check for SIM changes first. Cifas's Fraudscape 2025 report, published 7 May 2025, found unauthorised UK SIM swaps rose 1,055% in 2024; each swap hands the victim's bank codes to someone else.
Four numbers decide whether a ban is practical. Two come from that Cifas release; two are our arithmetic from the UAE and NIST documents.
UK SIM Swaps in 2024
Nearly 3,000
Each one hijacks your bank texts
Takeovers Hitting Phone Accounts
48%
Your number is the target
UAE Cut-Over Window
8 months
Derived: a whole market switched
Extra Kit for a Passkey
£0
Derived: your phone already qualifies
The cost card kills the banks' usual excuse. NIST permits exportable keys at AAL2, its middle assurance level, and bars syncable authenticators only at AAL3, so on our reading a synced passkey on your phone clears the bar.
When nearly half of account takeovers involve a mobile phone account, a code sent to that phone is not a second factor. It is the same weak point, asked twice.
Britain already legislates security floors when advice fails, as its ban on default passwords in connected devices shows, and NIST is extending identity rules to AI agents that log in on your behalf. Bank logins remain the gap.
Which countries have made an SMS OTP ban law?
Four markets in our compilation compel banks to move customers off texted codes, namely the UAE, Singapore, Malaysia and the Philippines, while the UK and the US still treat the switch as advice rather than law.
Singapore's date is from the Monetary Authority of Singapore's 9 July 2024 release; the others are as reported by Newsonair, Bernama and the Daily Tribune. Britain's NCSC said on 23 April 2026 that passkeys "should now be consumers' first choice of login", but set banks no date.
| Market | Rule and date | What it means for you |
|---|---|---|
| ⏱ UAE | SMS and email codes gone by 31 Mar 2026 | App or face check approves payments |
| 🔒 Singapore | Login codes phased out from July 2024 | Activated token logs you in instead |
| ⚖️ Malaysia | Banks ordered off SMS codes, Sept 2022 | Major banks reported done by July 2023 |
| ⚖️ Philippines | Risky transfers off SMS from 25 June 2026 | Texts still allowed for balance checks |
| ⚖️ UK and US | Advice only, no removal date | Text code stays until you change it |
The UAE finished inside one UK financial year; the Philippines, whose circular dates to May 2025, gave banks about 13 months. Our call: a UK regulator could set a 12-to-18-month deadline, asking nothing the Gulf and Southeast Asia have not already done.
If you bank in the UK or US, you are in the third of these markets where no rule removes the text code. Our count from the sources above; compelling means a published rule with a date.
Worked example: assume six logins: current account, savings, credit card, PayPal, pension and email. Four (current account, credit card, PayPal, email) accept a texted code alone. One SIM swap reaches 4 of 6, two thirds. Move email and current account to passkeys: 4 minus 2 leaves 2 of 6, one third, halving your exposure.
Now do your own one-swap count: list your money and email logins and count those that accept a text code alone. That number, found in under a minute, is your exposure today.
Would banning text codes lock out people without smartphones?
No, a ban written NIST's way removes the texted code as a sole factor while requiring services to keep other authenticator types open to every customer, so nobody depends on a smartphone.
NIST requires that "alternative authenticator types are available to all subscribers" and that verifiers "SHALL offer at least one phishing-resistant authentication option at AAL2". Texts survive as one route, never the only one. But SP 800-63 binds US federal agencies, not private banks.
Hardware is the fairer objection: passkeys need a phone that still gets updates, which is why we argued devices should print their end-of-support date at the point of sale. Recovery is the real grey area. If a lost phone means the bank lets you back in by text, the weakness returns by the side door. Our view, only an opinion: the fallback should be slower, not weaker (a branch visit, say, or frankly anything a phone shop cannot redirect).
Watch for these:
- Silent fallbacks: some passkey apps still accept a text via "try another way".
- Email resets: email recovered by text undoes your passkeys.
- Lockout: with no second device or backup codes, removing texts can lock you out.
- Number ports: ask your network what it checks before moving your number.
Key Takeaways to act on: check your own setup
- Your bank app offers passkeys, yet still lets you pick a text.
- Your email recovery number is the one your bank texts.
- You do not know what your network checks before issuing a SIM.
- You have no second device or backup codes for your bank.
SMS codes should be banned as the sole second factor for UK bank logins, with a deadline: the markets that did it finished in about a year, and alternatives, not texts, protect people without smartphones. Until then, set the rule yourself this week: turn on a passkey or in-app approval in your bank's app, switch off the text-only route, then do the same for your email. No second device or backup codes? Keep the text option until you have one. The NCSC's passkeys guide (undated, retrieved 23 October 2026) shows how.
How we checked this
We read NIST SP 800-63B-4 (page dated 26 August 2025) and its Authenticator Assurance Levels section, plus the Cifas Fraudscape 2025 release of 7 May 2025 and the regulator releases and reports cited above. The worked example assumes six logins, four protected by a texted code alone. No product was tested hands-on for this article. Last verified: 23 October 2026.
Edited by Sheftali, reviewed after publication. Spotted something out of date? Tell us and we will correct it.
No comments
Post a Comment